Retest a finding
Retest verifies that a vulnerability is fixed. It re-runs the original attack against your app and updates the finding. A retest is free: it does not use a credit and does not start a new pentest.
Retests are available for a limited period after the pentest (the retest window). Once it closes, the button says so, and a new pentest covers it.
Retest one finding
- Open Findings and select the finding.
- Click Re-test in the details panel.
- The finding shows Re-testing while it runs. The result lands in the finding when it finishes: Fixed if the attack no longer works, or still Open with fresh evidence.
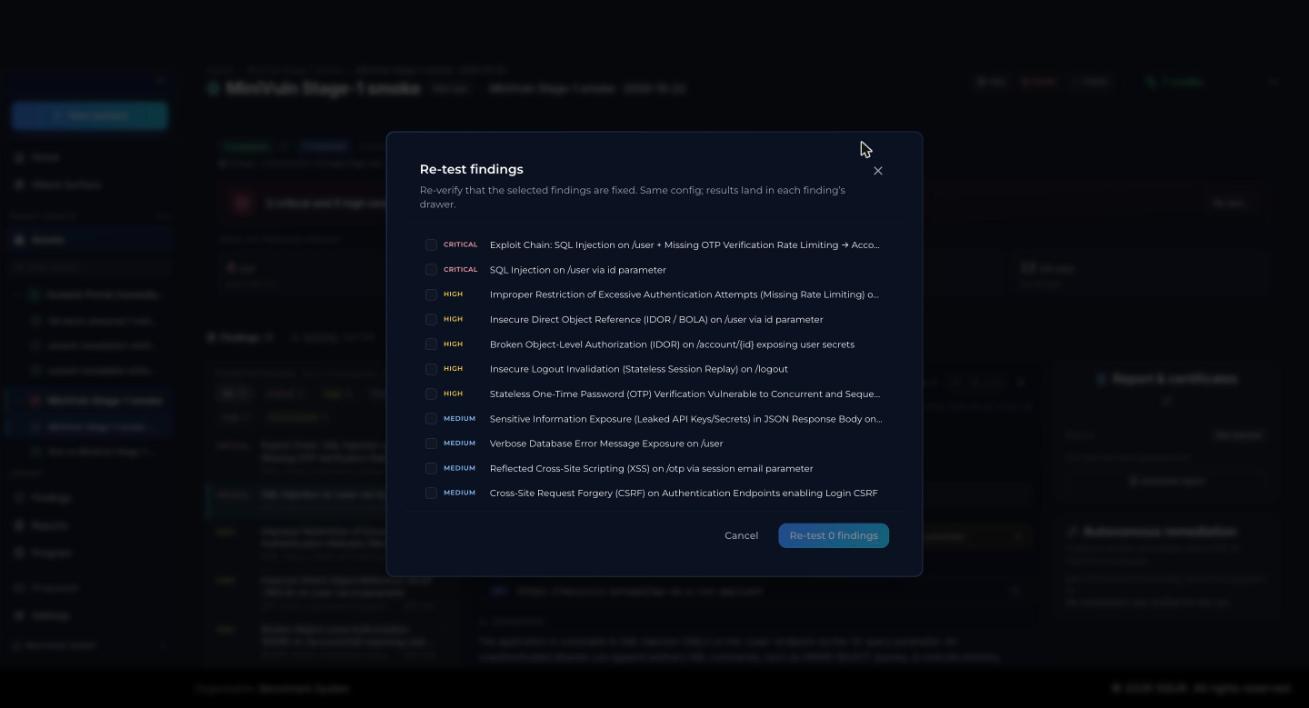
Retest several findings
- Open the run.
- In the run header, click Retest fixed (preselects the findings you marked fixed) or Retest....
- Check the findings you want and start the re-test.
What happens next
- A finding that was fixed and later comes back is shown as Regressed.
- The next pentest on the same app also re-checks open findings first, before looking for anything new.
- Regenerate your report afterwards so it reflects the retest results.