Whitebox pentest: add your source code
A pentest without source code is black-box: SQUR attacks your running application from the outside. Add your source code and the same pentest becomes whitebox: SQUR reads the code and tests the running application, which finds more and explains findings down to the file. There is no extra charge.
Two ways to provide code
Both are in the Source code card of the pentest setup, between Scope and API spec.
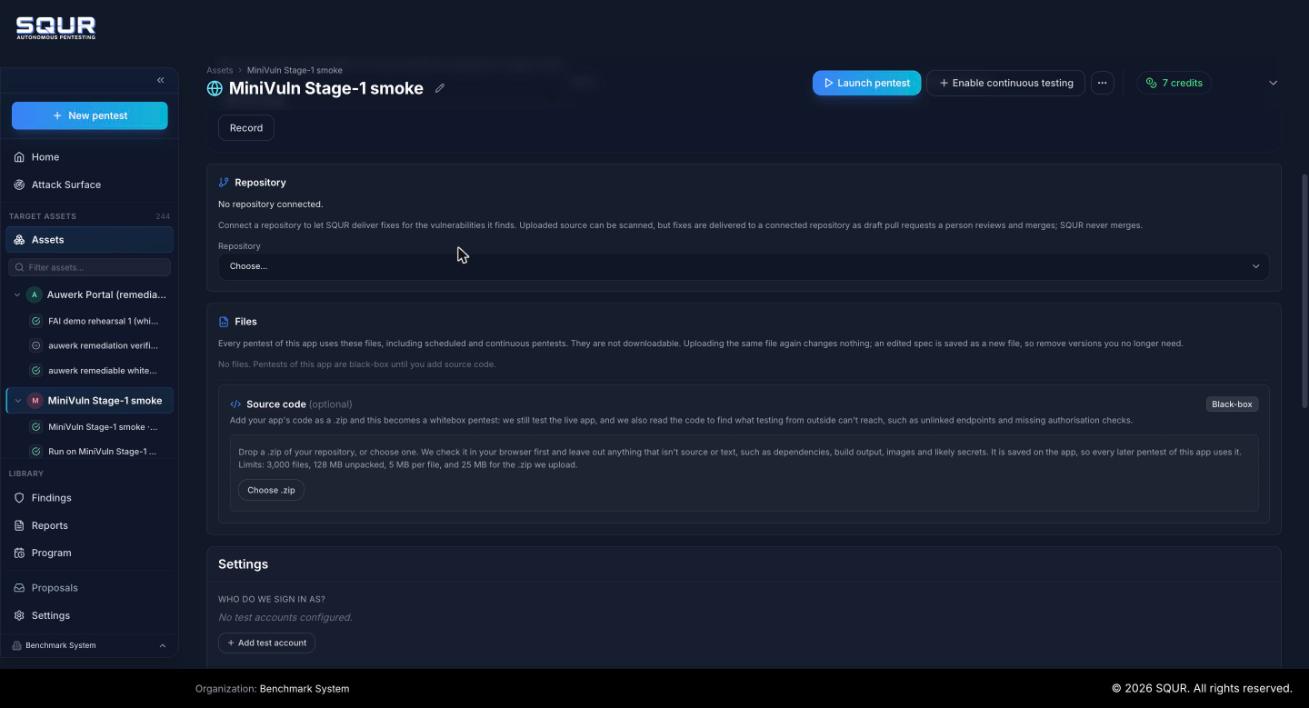
Upload a zip
- Drop a
.zipof your repository on the card, or choose one. - SQUR cleans the archive in your browser before anything is uploaded, and shows you what it left out.
- Review the summary (file count, languages, excluded folders) and continue.
Left out automatically:
- system files and build output, and dependencies,
- everything your
.gitignorematches, - possible secrets: credential files and private keys,
- symbolic links, unsafe paths, binary and non-text files, files over the per-file size limit, and unreadable or encrypted files.
You can also deselect folders yourself.
Connect a GitHub repository
Where repository access is enabled for your organization, the card offers a repository picker. An administrator installs the SQUR GitHub App on the repositories they choose. The app can read contents and metadata of those repositories, nothing else. Every later pentest fetches the current branch at launch, so you do not upload a new archive when the code changes. The branch is checked at every launch.
Saved on the app
Source code is saved on the app, so every later pentest of that app uses it, including scheduled and continuous ones. Without source code, pentests of the app stay black-box. If your code changed, replace the archive.
What the pentest does with it
The pentest uses the code alongside the live application. A finding is still reported only when it is exploited against the running application, so whitebox does not add unproven findings.
Autonomous remediation builds on the same source code.
Data handling
Source code is processed in the EU. Disconnecting a repository removes SQUR's access to it. See Security for defenders and the SQUR Trust Center for the full data handling terms.